
Direct Links | Infosec News Feeds
The San Francisco Beat
SFInfoSec aggregates the latest news, podcasts and books covering Cyber Security, Hacking, Infosec, Online Privacy, Cryptography, Threat Research and Vulnerability Disclosures from all the leading sources.
Threatpost The First Stop For Security News
- Student Loan Breach Exposes 2.5M Records
 by Nate Nelson on August 31, 2022 at 12:57 pm
2.5 million people were affected, in a breach that could spell more trouble […]
- Watering Hole Attacks Push ScanBox Keylogger
 by Nate Nelson on August 30, 2022 at 4:00 pm
Researchers uncover a watering hole attack likely carried out by APT TA423, […]
- Tentacles of ‘0ktapus’ Threat Group Victimize 130 Firms
 by Nate Nelson on August 29, 2022 at 2:56 pm
Over 130 companies tangled in sprawling phishing campaign that spoofed a […]
Krebs on Security In-depth security news and investigation
- Data Broker Radaris Loses Domains in Privacy Fight
 by BrianKrebs on September 16, 2026 at 6:14 pm
The consumer data broker Radaris.com has long had a reputation for ignoring […]
- Microsoft Plugs Nearly 1,000 Security Holes
 by BrianKrebs on September 8, 2026 at 9:44 pm
Microsoft Corp. today issued updates to plug at least 974 security holes in its […]
- FBI Probes Service Selling 153M+ Drivers Licenses
 by BrianKrebs on September 1, 2026 at 10:40 pm
A new identity theft service launched on the dark web this week is selling […]
darkreading Public RSS feed
- [Virtual Event] Cybersecurity Outlook…
 on December 3, 2026 at 4:00 pm
- Microsoft Disrupts EvilTokens Device…
 by Alexander Culafi on September 22, 2026 at 8:02 pm
Microsoft seized 50 websites and disabled more than 150 domains as part of a […]
- Shai-Hulud Attack Nips Cyber-Firm…
 by Elizabeth Montalbano on September 22, 2026 at 5:32 pm
Threat actors stole 170 private repositories using an OAuth token stolen from a […]
Blog RSS Feed Fortra Blog
- 3 Years In: How Is AI Doing? SANS Weighs In
 by Katrina Thompson on December 15, 2025 at 8:09 am
It’s no secret that AI is “here.” It’s been here for three years now, […]
- What Is Log Management and Why you Need itby Anirudh Chand on November 24, 2025 at 6:00 am
It is arguable that log management forms the basis of modern cybersecurity. […]
- What Did We Learn from the NCSC’s 2025 Annual Review?by Josh Breaker-Rolfe on November 21, 2025 at 11:47 am
Earlier this year, the UK’s National Cyber Security Centre (NCSC) released […]
Security Latest Channel Description
- A New Tool Found Malware That’s Guided by an AI Hive Mind—No Humans in Sight
 by Lily Hay Newman on September 22, 2026 at 10:00 am
Cisco Talos researchers created a new framework for identifying malware and […]
- How to Use AI With Your Privacy Intact
 by Andy Greenberg on September 22, 2026 at 9:00 am
Your conversations with AI chatbots are both highly personal and deeply […]
- US and China Discuss Alerting Each Other to AI National Security Threats
 by Isabella Ward on September 21, 2026 at 10:34 am
Officials discussed setting up a mechanism for the two countries to notify each […]
- 7MS #740: Tales of Pentest Pwnage – Part 90by Brian Johnson on September 18, 2026 at 6:30 pm
Hey friends! We’ve been on a bit of a Tales of Pentest Pwnage bender lately, […]
- 7MS #739: Tales of Pentest Pwnage – Part 89by Brian Johnson on September 11, 2026 at 8:16 pm
Hey friends! Today is a tale of pentest pwnage episode, and this one features […]
- 7MS #738: Baby’s First ProjectDiscovery Neoby Brian Johnson on September 4, 2026 at 4:59 pm
Hey friends! Today I’m talking about Baby’s First Neo — and to be crystal […]
- GPT-6 Astra Breaks an Old Enigma Messageby Bruce Schneier on September 22, 2026 at 11:02 am
This is pretty amazing: However, the most astonishing thing about this break is […]
- Reverse-Engineering Flock Camerasby Bruce Schneier on September 21, 2026 at 2:37 pm
Hackers captured a Flock camera and got a look (alternate link) at the […]
- Friday Squid Blogging: On Squid Egg Sacsby Bruce Schneier on September 18, 2026 at 9:06 pm
Short essay about squid egg sacs. As usual, you can also use this squid post to […]
GRAHAM CLULEY Cybersecurity keynote speaker
- US Coast Guard and FBI board oil tanker to investigate cyber attackby Graham Cluley on September 17, 2026 at 2:43 pm
An oil tanker bound for Texas was boarded mid-voyage by the US Coast Guard and […]
- Smashing Security podcast #485: These researchers got drunk to hack an LG TVby Graham Cluley on September 16, 2026 at 11:07 pm
Researchers wanted to test if LG’s smart TVs come with any security risks – but […]
- Former AT&T store worker jailed after moonlighting as a SIM-swap gang’s…by Graham Cluley on September 15, 2026 at 9:43 am
44-year-old Kenneth Carter from Portland, Oregon, used to work in an AT&T […]
BleepingComputer BleepingComputer – All Stories
- Chinese hackers exploit WordPress, Zyxel flaws to steal govt databy Bill Toulas on September 22, 2026 at 8:35 pm
A Chinese-speaking threat actor has been exploiting vulnerabilities in ZyXEL […]
- ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breachby Lawrence Abrams on September 22, 2026 at 7:13 pm
The ShinyHunters extortion gang claims it breached FBI systems using a new […]
- New ClosedQuorum Windows malware uses AI for attack decisionsby Bill Toulas on September 22, 2026 at 6:04 pm
A new Windows malware named ClosedQuorum uses Google Gemini, DeepSeek, Qwen, […]
TechCrunch Startup and Technology News
- Qualcomm launches two new smartphone chips with emphasis on AIby Ivan Mehta on September 22, 2026 at 8:00 pm
Qualcomm said that its new top chip can run 30B mixture-of-expert model locally.
- Apple could take on Whoop with a new fitness tracker, report saysby Lucas Ropek on September 22, 2026 at 7:27 pm
Apple may be developing a new fitness tracker as part of its new generation of […]
- Meta admits Muse’s likeness to OpenClaw isn’t a coincidenceby Sarah Perez on September 22, 2026 at 7:09 pm
Meta says Muse was built from scratch, but acknowledges the AI assistant was […]
The Hacker News Most trusted, widely-read independent cybersecurity news source for everyone; supported by hackers and IT professionals — Send TIPs to [email protected]
- Check Point Warns of Management Server Zero-Day Exploited in Targeted Attacks
 by [email protected] (The Hacker News) on September 22, 2026 at 6:29 pm
Attackers exploited a previously unknown flaw in Check Point’s Security […]
- WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on…
 by [email protected] (The Hacker News) on September 22, 2026 at 6:03 pm
WordPress has fixed a critical flaw in its core software that lets an attacker […]
- Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate…
 by [email protected] (The Hacker News) on September 22, 2026 at 5:58 pm
Cybersecurity researchers have disclosed details of a malicious npm package […]
The DFIR Report Actionable Cyber Threat Intelligence
- BengalSEO Part 1: Anatomy of the Operationby editor on August 24, 2026 at 2:28 pm
Key Takeaways The DFIR Report Offerings Check out our Products here and our Services here. Want a demo, more information on our services, pricing or just want to chat? Get in Touch Contact us today for pricing or a demo! Case Summary In March 2026, our team identified an SEO poisoning campaign leading to malware deployment The post BengalSEO Part 1: Anatomy of the Operation appeared first on The DFIR Report.
- From Bing Search to Ransomware: Bumblebee and AdaptixC2 Deliver Akiraby editor on June 29, 2026 at 1:07 pm
Key Takeaways This case was first reported to customers in a threat brief released in July 2025 and in a public flash alert in August 2025 in partnership with Swisscom B2B CSIRT, which observed another intrusion tied to the same campaign. This report contains data from both intrusions. We plan to release a DFIR Labs The post From Bing Search to Ransomware: Bumblebee and AdaptixC2 Deliver Akira appeared first on The DFIR Report.
- Flash Alert: EtherRat and TukTuk C2 End in The Gentleman Ransomwareby editor on May 11, 2026 at 2:05 pm
The EtherRAT malware family was first reported by Sysdig back in December 2025. At that time, the initial access vector was exploitation of CVE-2025-55182 (React2Shell) targeting Linux servers. In March 2026, a Windows variant campaign was reported by Atos, with their investigation showing evidence of activity going back to the previous December. In April, we The post Flash Alert: EtherRat and TukTuk C2 End in The Gentleman Ransomware appeared first on The DFIR Report.
Biz & IT – Ars Technica Serving the Technologist since 1998. News, reviews, and analysis.
- Microsoft disrupts AI-assisted platform that compromised 12,000
 by Dan Goodin on September 22, 2026 at 7:45 pm
EvilTokens provided an end-to-end platform that makes mass compromises faster […]
- IT mistake erases 11 years of viewing history for hospitals’ maternity records
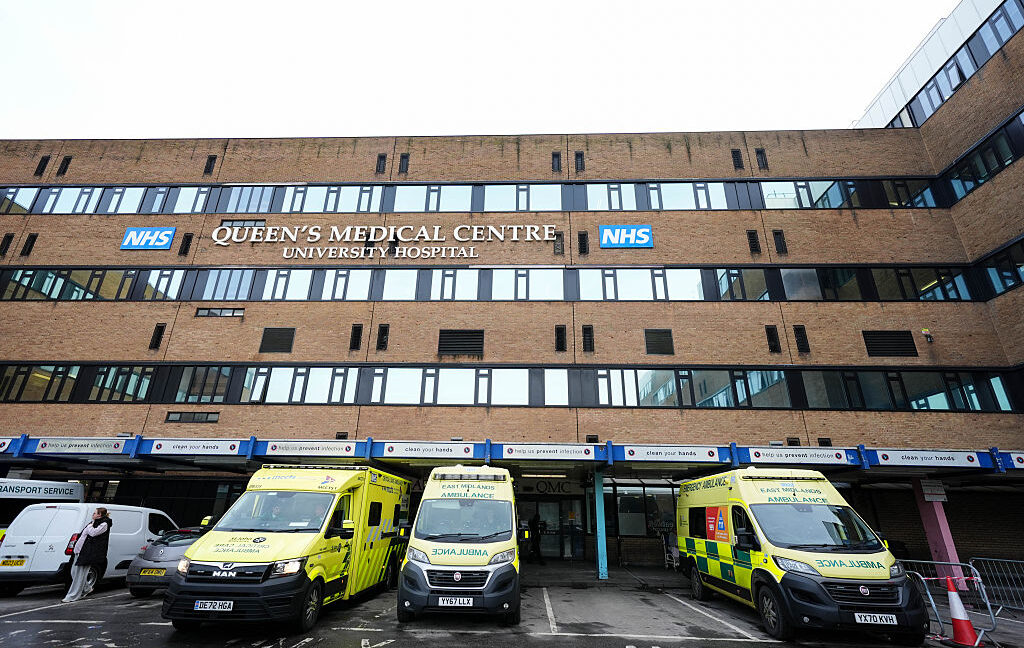 by Scharon Harding on September 22, 2026 at 4:55 pm
The English hospitals recovered patient care data only.
- Muse, Meta’s extraordinarily privileged AI assistant, has a serious 0-day
 by Dan Goodin on September 21, 2026 at 10:24 pm
A simple ClickFix attack is only one way to completely hijack the new agent.
Websec Cybersecurity Blog Expert insights, trends, research findings, and best practices from Websec security team to help you strengthen your organization’s security posture.
- A Comparison Between the Real User ID and the Effective User ID is not Enough to Prevent Privilege Escalationby Websec Security Team on October 3, 2023 at 7:39 pm
In Unix-like systems, processes have a real and effective user ID determining their access permissions. While usually identical, they can differ in situations like when the setuid bit is activated in executables.
- Websec DevSecOps Webinarby Websec Security Team on August 29, 2022 at 12:00 am
Roberto Salgado and Kobalt.io’s Miki Fukushima are hosting a free webinar on September 20, 2022 covering why application security matters, the shift to developer-first security, and a practical roadmap for embedding security into DevSecOps.
- CVE-2022-21404: Another story of developers fixing vulnerabilities unknowingly because of CodeQLby Websec Security Team on May 19, 2022 at 6:18 pm
How CodeQL may help reduce false negatives within Open-Source projects. Taking a look into a deserialization vulnerability within Oracle Helidon (CVE-2022-21404).